Security at Quorel
Your people’s most
Your people’s most
important data
deserves the highest Care.
Salaries. Bank accounts. PAN and Aadhaar numbers. Home addresses. Medical leave. We protect the information entrusted to Quorel People with encryption for sensitive fields, two-factor sign-in, server-enforced access and an audit trail of sensitive actions.
Documented controlsSee how each layer works
Privacy by designAccess follows assigned roles
Talk to an engineerDirect answers to security questions
AES-256-GCMSensitive fields
Two-factorSign-in security
Role-basedServer-checked access
Audit trailSensitive actions
Our Security Principles
Built on trust. Protected by Design.
Your people’s data deserves the highest standard of security. Here’s how we keep it safe at every layer.
Data Security
Encryption for
Encryption for
the fields that matter
Transport is TLS. Sensitive fields — bank account numbers, PAN, Aadhaar and two-factor secrets — are encrypted with AES-256-GCM before they reach the database.
- Authenticated encryption detects tampering
- AES-256-GCM encryption at rest
- Encryption keys kept outside the database
- Passwords hashed with bcrypt, cost 12
Access Security
Two-factor
Two-factor
sign-in
Add a second factor with an authenticator app or a one-time email code. The authenticator secret is itself encrypted, so it is never stored as readable text.
- Authenticator apps or one-time email codes
- Sign-in, reset and contact forms rate limited
- Account lockout after repeated failures
- Consistent errors protect account privacy
Access Control
Access decided
Access decided
on the server
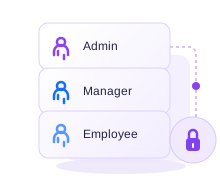
Roles are not a UI preference. Every request is checked against your role and scope before data is read or written. A hidden button is not the same as a blocked API.
- HR, payroll, IT, finance and manager roles
- Permissions checked on every request
- Managers see only their reporting line
- Short-lived signed links for uploaded files
Audit & accountability
An audit trail with
An audit trail with
a “why” column
Sensitive actions record who did what, what changed, when and from where. Operator actions include a reason where required, so salary edits and payroll approvals are attributable.
- Old and new values retained
- IP address and user agent recorded
- Reasons captured where required
- Readable by your own admins — your log
Data Isolation
One company
One company
cannot see another
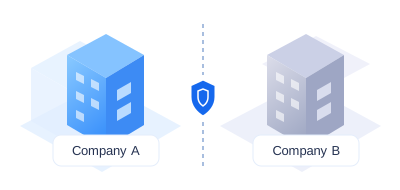
Every record belongs to a company, and every query is scoped at the data layer — not filtered afterwards in the interface. A customer account cannot reach another company’s data by changing a URL.
- Tenant scope applied server-side on read and write
- Unrecognised plans and suspended companies are refused, rather than defaulted open
- Regression tests guard against permissions quietly loosening
Infrastructure Security
Our own access
Our own access
is fenced too
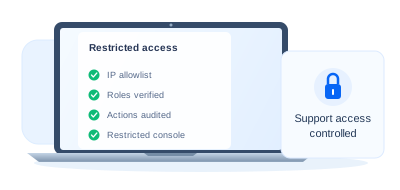
Our operator console is a separate, restricted surface. Access can be locked to specific IP addresses, actions are audited, and support access to your workspace is recorded rather than ambient.
- Operator access gated by an IP allowlist in production
- API hardening: security headers, rate limits and outbound SSRF guards
- Support actions are recorded and attributable to the operator
Being Straight with You
What we do Not Claim.
Quorel Technologies does not hold SOC 2, ISO 27001 or any other third-party security certification today, and we will not imply otherwise with a badge on a page. What is written above is what is built and running — no more.
We also will not tell you encryption makes data unbreakable. What it guarantees is that the plaintext is unrecoverable without the key, and the key is not stored beside the data. That is a real, bounded promise, and we would rather give you one of those than a large vague one.
If your procurement process needs a security questionnaire filled in, a DPA signed, or a call with whoever wrote the access-control layer, ask. You will get an engineer, not a form letter.
TransparentNo security marketing.
Open conversationsTalk to real engineers.
Clear and honestExactly where we stand.
Responsible Disclosure
Found something? Tell us Before You Tell Anyone Else.
If you believe you have found a security issue in Quorel, please report it to support@quorel.in with “Security” in the subject line. Include what you found, how to reproduce it, and what you think the impact is.
We will acknowledge your report, keep you updated while we work on it, and credit you if you would like. Please do not access, modify or exfiltrate anyone else's data while testing, and give us a reasonable window to ship a fix before publishing.
Get Started
Have your security team read this
Have your security team read this
page and come back with questions.
That is the sales process we prefer. Bring the hard ones.